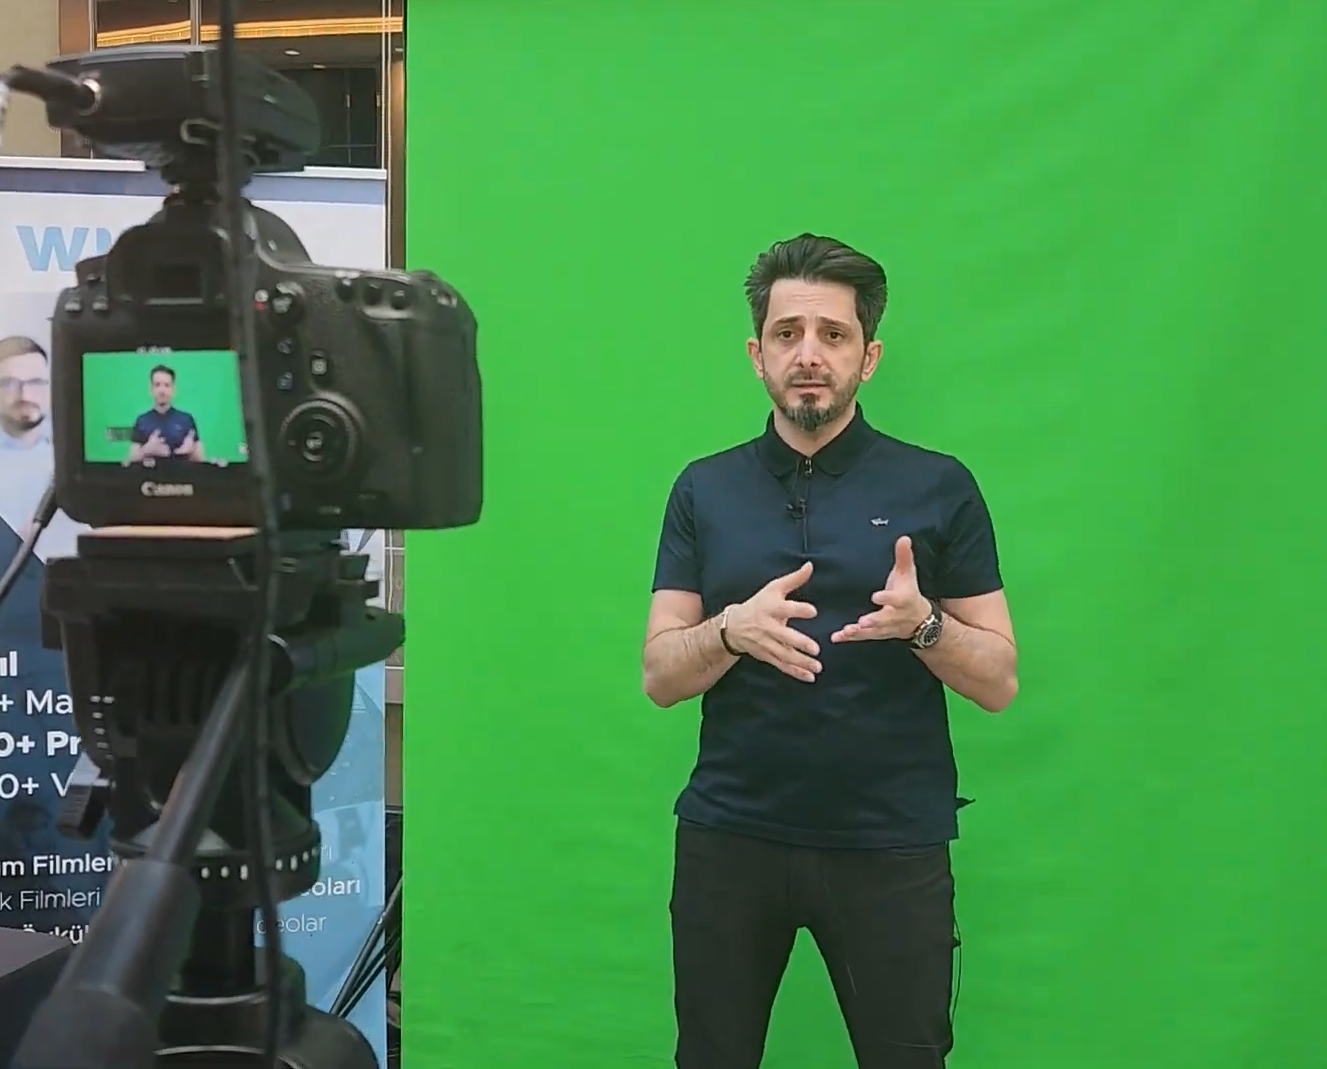
Ayşim Niksarlı, Director of Cybersecurity Consulting Services at Forcerta, met with students at the 2024 Cyber Summer Camp, organized by BÜSİBER (Boğaziçi University Management Information Systems Cybersecurity Center) and the Union of Cyber Clubs.
Ayşim Niksarlı stated the following:
GRC stands for “Governance, Risk, and Compliance.” This concept encompasses the processes of governance, risk management, and compliance within organizations. The primary objective of GRC is to ensure that companies maintain effective management across various domains, with a particular focus on information security.
Governance:
Governance refers to the management processes within an organization, covering a wide range of areas, including information security. It ensures that policies and procedures established across the organization are known and implemented by everyone. This also includes keeping senior management informed, measuring processes through specific metrics, and pursuing continuous improvement. Governance defines the overall framework for a company and enhances the effectiveness of its management processes.
Risk Management:
Risk management determines how an organization handles the risks it may encounter. When addressing risks, various strategies can be applied, such as eliminating, transferring, mitigating, or accepting them. Prioritizing risks and determining their level of criticality is essential for effective risk management. In the context of information security, when deciding where to allocate investments, the focus should be on identifying the most critical risks and addressing them promptly.
Compliance:
Compliance is of great importance, especially in regulated sectors. Companies have an obligation to provide the best and most reliable services to their customers. In addition, they must comply with various regulations and laws. For instance, legislation such as the KVKK (Personal Data Protection Law) and the GDPR (General Data Protection Regulation), as well as sector-specific regulations—such as the regulation on information systems for banks issued by the BRSA (Banking Regulation and Supervision Agency)—are rules with which companies must ensure compliance.
GRC enables companies to effectively manage their governance, risk management, and compliance processes. These processes are of critical importance to a company’s sustainability and reliability.
About the Wise
Similar Videos from this Wise
What Strategies Should Be Used to Continuously Monitor Supplier Risks?
Ayşim Nikralı, Director of Cybersecurity Consulting Services at Forcerta, spoke about the strategies that should be followed...
Where should organizations begin with risk management?
In an interview with Wise TV, Ayşim Niksarlı, Director of Cybersecurity Consulting Services at Forcerta, discusses the fundam...
Why is data governance important in terms of data security?
In an exclusive interview with Wise TV, Ayşim Niksarlı, Director of Cybersecurity Consulting Services at Forcerta, offers a [...