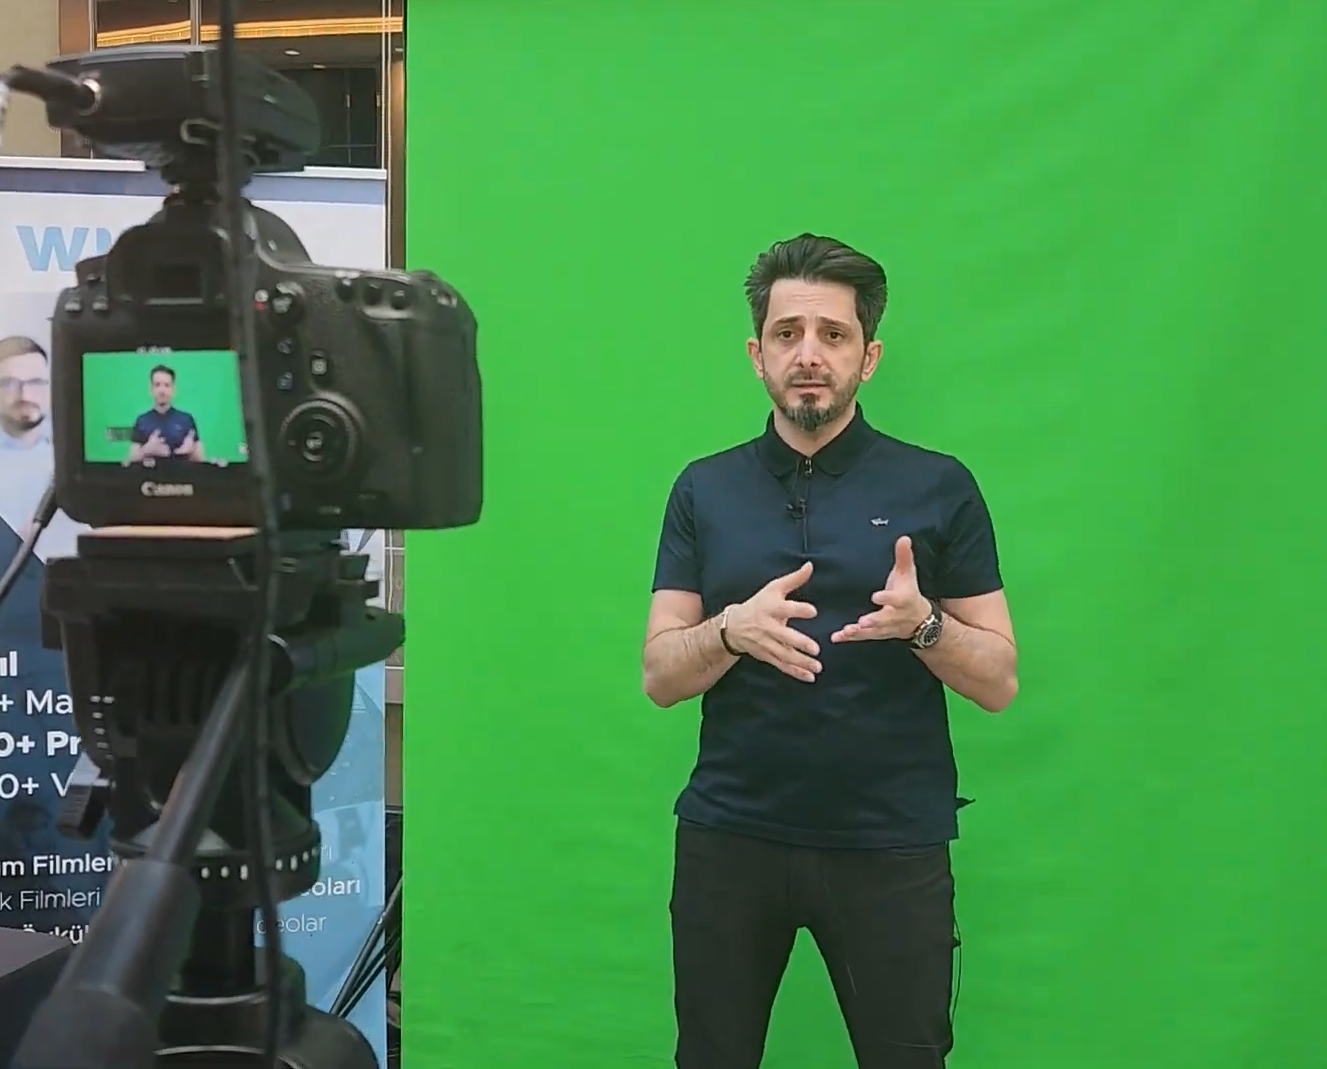
In an interview with Wise TV, Emre Erkıran, Information Security Manager at QNB Invest, explained the critical role of KPIs (Key Performance Indicators) in information security management.
KPIs are of great importance from a management perspective. When an internal investment is proposed or attention needs to be drawn to risk management, KPIs are essential for explaining the situation and securing buy-in. For instance, metrics such as incident response times, the number of vulnerabilities, the speed at which specific vulnerabilities are remediated, and patch application status can be tracked using KPIs. Additionally, compliance with internal regulations and policies, the encryption rate of sensitive data, employee completion rates for awareness training, and the results of social engineering tests serve as important metrics.
While these metrics may vary from one organization to another, they generally play a critical role in both persuading senior management and assessing the organization’s information security posture. By providing visibility, KPIs make management processes more effective and facilitate strategic decision-making.
About the Wise
Similar Videos from this Wise
What are the defense strategies against AI-powered cyber threats?
In an exclusive interview with Wise TV, QNB Invest Information Security Manager Emre Erkıran discussed the impact of [&hellip...
What measures should businesses take against third-party attacks?
Speaking to Wise TV, Emre Erkıran, Information Security Manager at QNB Invest, discussed the strategic importance and securit...