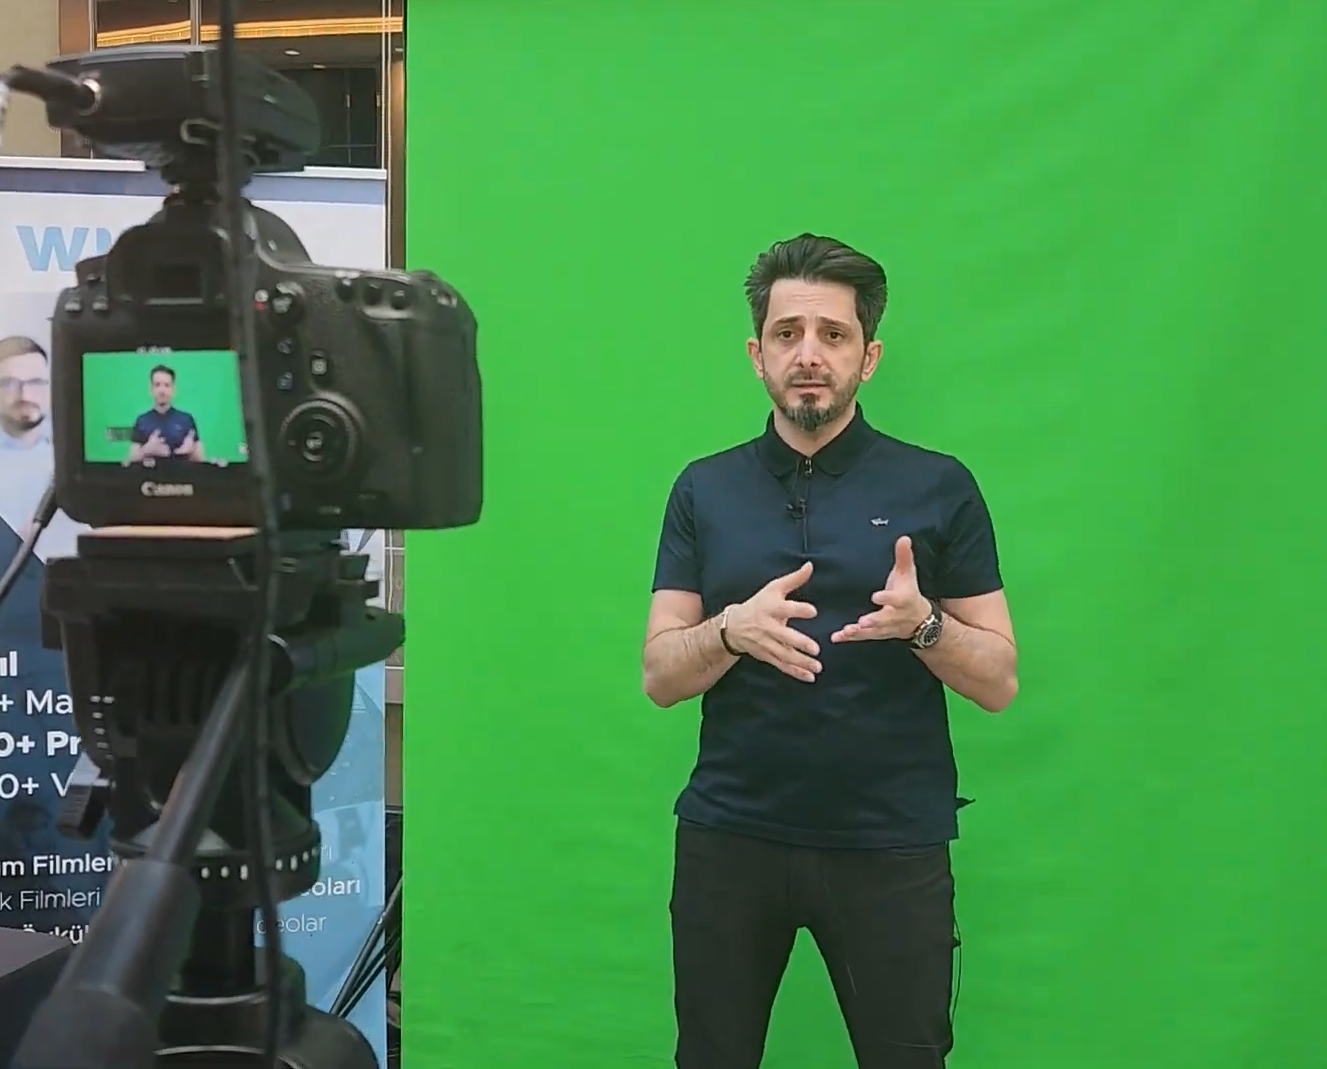
In this exclusive interview with Wise TV, Harun Öztürk, Country Manager for Sangfor Technologies Turkey, explains in detail:
🔹 Sangfor’s advanced Next-Gen Firewall (NGFW) solutions
🔹 The Neural-X AI-powered threat analysis infrastructure
🔹 The capabilities of the Internet Access Gateway (IAG) product, such as content filtering, quota management, and access control
🔹 The scalable architecture designed for SMBs as well as medium- and large-scale enterprise networks
🔹 Access policies compliant with KVKK and GDPR regulations
Hello and welcome. Today, I will tell you about SF Network Secure and our internet access gateway. I hope you find this presentation engaging. I am Harun Öztürk, and I work as the Country Manager at SF. SF is a manufacturer that offers a wide range of highly competitive firewall products. You are likely aware of the current state of the networking world and the broader landscape we live in; we face numerous attacks, and the nature of these attacks is evolving. We are moving beyond the traditional signature-based attacks we once knew toward attacks driven by complex algorithms. On average, over 400,000 new malware variants emerge daily, and we are all exposed to them—often without even realizing it. However, through our in-house R&D efforts, we continuously innovate and expand our product portfolio to include both signature-based detection and behavioral analysis capabilities. In our firewall ecosystem, we go beyond traditional firewalls by utilizing a model called “Neural-X,” which detects threats via the cloud; this allows us to respond to threats more dynamically, effectively, and rapidly. There is a great deal to discuss regarding our firewalls, so I will try to pick up the pace a bit. As I mentioned earlier, approximately 400,000 to 450,000 new malware variants appear every day. We employ an AI engine called “Engine Zero” to address these threats, enabling our firewalls to take dynamic action against all types of malware. Overall, our firewall solutions cater to a broad audience. We offer hardware appliances, as well as virtualized versions that can be deployed on hypervisors. Beyond that, however, we offer solutions positioned for the SMB and mid-market segments, as well as for the high-end enterprise sector. As for SF, we are a Chinese manufacturer and have been featured in the Gartner Magic Quadrant for eight years. For the past two years, we have consistently been recognized as a “Visionary” in the industry—a position that fills us with pride and marks significant progress. Furthermore, our product receives exceptionally high ratings from Cyber Ratings in the enterprise sector, placing it firmly in the category of high-value-added solutions. Beyond our technical capabilities—and we are extremely confident in our technology, backed by a team of over 3,000 R&D personnel—we offer a substantial cost advantage; in today’s world, where every penny counts, we deliver significant value to our customers. As I mentioned, the product incorporates “Neural-X,” a cloud-based, self-learning threat intelligence system. We currently recognize over a billion malware variants, and with millions of new threats emerging daily, our system rapidly learns from and responds to them. As noted, approximately 450,000 new malware samples appear regularly. I emphasize malware because firewalls are sometimes overlooked in this context; people assume that simply having a firewall in place is enough, but the critical question is: how effectively does that firewall keep up with the latest updates and defend against emerging attacks? This is a vital aspect, and it is a top priority for us. Our product goes beyond traditional signature-based detection to employ a self-learning architecture—a capability that extends to our WAF module as well. In short, we offer a dynamic, evolving system that provides a superior layer of defense against all manner of threats. Another often overlooked area—or one we may not be fully aware of—is vulnerability. In the IT backend—behind the firewalls—there are numerous products, solutions, and applications used by your organization; these can harbor vulnerabilities or lack necessary updates. You might have installed a device years ago and never updated it—perhaps for eight or ten years. We scan for these vulnerabilities and can provide you with individual reports on them. This is a significant capability for us. One of the key strengths of our firewall is that it comes from a dedicated cybersecurity company. We also have our own EDR solution; when used in tandem, the firewall communicates with the EDR, enabling much faster responses to threats. If we look at a typical use case—considering a standard infrastructure—we have servers, a firewall positioned in front of them, and a system operating based on the policies and criteria you have defined for inbound traffic. However, this setup can be expanded to include features like URL and content filtering; this is where our additional solutions come into play. By integrating our various products, we can provide a much more robust security layer. Let’s examine the firewall itself, and then I will introduce another new product and explain how it integrates with the firewall. Beyond standard firewall capabilities, our solution includes specific protections against ransomware threats. It enables rapid action, allowing you to neutralize any threat very quickly; it offers you capabilities such as these. It is designed for use in Security Operations Centers (SOCs), facilitating swift responses. Let me also touch upon the Internet Access Gateway (IAG) component that integrates with this system. Essentially, we are discussing two distinct products here: a firewall and an Internet Access Gateway. To visualize the IAG, you can think of it as a web proxy. Before diving into the specific features, I should note that while we believe using them together yields high efficiency, the IAG does not strictly require our firewall to be positioned in front of it. If you already have an existing firewall but need an IAG behind it, we can deploy our product in that configuration as well. Its core features include filtering, content filtering, and web traffic management. A common question arises here: “We already have a firewall; doesn’t it handle these tasks?” While firewalls do perform these functions, placing the entire load on the firewall in high-traffic environments creates a risk of bottlenecks. To minimize this risk and enhance firewall efficiency, we can manage traffic by positioning the IAG in the background. Another key feature of the IAG is its ability to optimize high bandwidth usage—something you can also think of in terms of quota management. Let’s illustrate this with an example: Suppose you are a large organization with 500 employees. Consider that, during their downtime or when they are away from their desks, a significant number of them likely want to stream content or watch online videos. This activity consumes your organization’s bandwidth. We intervene in this traffic and optimize it through a fully customized, “tailor-made” approach—configuring settings specifically for individual departments or even specific users. Another key feature of the IAG solution is its support for two-factor authentication. Take a hospital or a hotel, for instance; while the facility relies on specific, mission-critical applications to operate, you also want to provide internet access and bandwidth to guests to ensure their satisfaction. We can balance these needs with a completely customized configuration. Furthermore, our IAG product is recognized by Gartner in this category. It offers multiple operational modes—such as bridge, route, and single modes—allowing us to position the product according to your organization’s specific network topology requirements. Regarding access control and internet usage, we can implement application-level controls—such as restricting access to certain applications while allowing others. For example, you could allow a user to watch YouTube but restrict them from posting comments. Alternatively, the system can dynamically adjust settings—for instance, allowing viewing between 8:00 AM and 12:00 PM but at a lower resolution to avoid excessive bandwidth consumption, while permitting higher resolution between 12:00 PM and 2:00 PM. Speaking of dynamic adjustments, let me shift the focus slightly with another similar example: imagine an organization with 100 employees. Bandwidth is used normally throughout the day, but as the clock strikes 5:00 or 6:00 PM, some people leave for home while others remain. Let’s assume 10 employees stay behind to work overtime. We can dynamically distribute the bandwidth unused by those 90 people to these 10 individuals, implementing this as a system policy or rule. We can manage quota usage in a similar fashion; for instance, we can configure scenarios where, upon exceeding a certain quota, a user is blocked from internet access, or—alternatively—allowed to access the internet but at a significantly reduced speed and within a restricted bandwidth allocation. Regarding the captive portal: as previously mentioned, we can present a captive portal to guest users, admitting them to the system via a dedicated guest network segment and granting them internet access. This capability is particularly valuable today, given the prominence of regulations like KVKK and GDPR and the resulting compliance requirements; it offers a highly efficient solution. By integrating the firewall and IAG products, we can perform content management and enforce URL or access restrictions. Thanks to “Neural-X”—our backend artificial intelligence—the system is continuously updated, ensuring your organization remains protected against the latest threats. Today, I have outlined SF’s firewall and internet access gateway solutions. I have done my best to explain these products, along with SF’s latest developments and the benefits they offer. Thank you very much for listening. I look forward to seeing you again in our next presentation to discuss our other solutions.
SF Network Secure and Internet Access Solutions
In today’s world, cybersecurity has become more critical than ever. With the widespread adoption of the internet and the acceleration of digitalization, cyber threats are on the rise. In this context, companies like SF Network Secure help businesses and individuals protect themselves against these threats by offering security solutions. SF Network Secure—where Harun Öztürk serves as Country Manager—stands out with its extensive product portfolio, particularly its firewall and internet access solutions. In this article, we will examine the solutions offered by SF Network Secure and their significance in the realm of cybersecurity.
Firewall Solutions
SF Network Secure provides effective security solutions to its users through a wide range of firewall products. Modern cyber attacks have evolved beyond simple signature-based methods into more complex attacks that incorporate sophisticated algorithms. Keeping pace with this evolution, SF protects its users with products that utilize both signature-based detection and behavioral analysis.
Neural-X Technology
One of the key innovations offered by SF Network Secure is Neural-X technology. Operating on a cloud-based model, this technology is capable of detecting a wide array of threats. Neural-X possesses the capacity to respond rapidly and dynamically to threats.
Engine Zero and Malware Protection
With over 400,000 new malware variants emerging daily, these threats pose a significant challenge in the cybersecurity landscape. SF provides dynamic protection against these threats through an AI-powered system known as Engine Zero. By undergoing continuous updates, this system offers an effective defense mechanism against emerging threats.
Internet Access Gateway Solutions
SF Network Secure also stands out with its internet access gateway solutions. These solutions provide users with a secure internet experience through features such as web traffic management and content filtering. Additionally, they enhance security levels with features like two-factor authentication.
High Bandwidth and Optimization
The internet access solutions offered by SF optimize high bandwidth usage, providing users with a more efficient internet experience. These solutions enable users to manage and optimize their internet traffic.
Security and User Experience
The solutions offered by SF Network Secure not only ensure security but also improve the user experience. Users can work efficiently in a secure internet environment and make the most of the opportunities the internet offers.
SF Network Secure has established a significant position in the cybersecurity world with its innovative solutions. Through its firewall and internet access solutions, it provides effective protection for users while simultaneously enhancing the user experience. Under the leadership of Harun Öztürk, SF Network Secure continues to play a pioneering role in the field of cybersecurity.
About the Wise