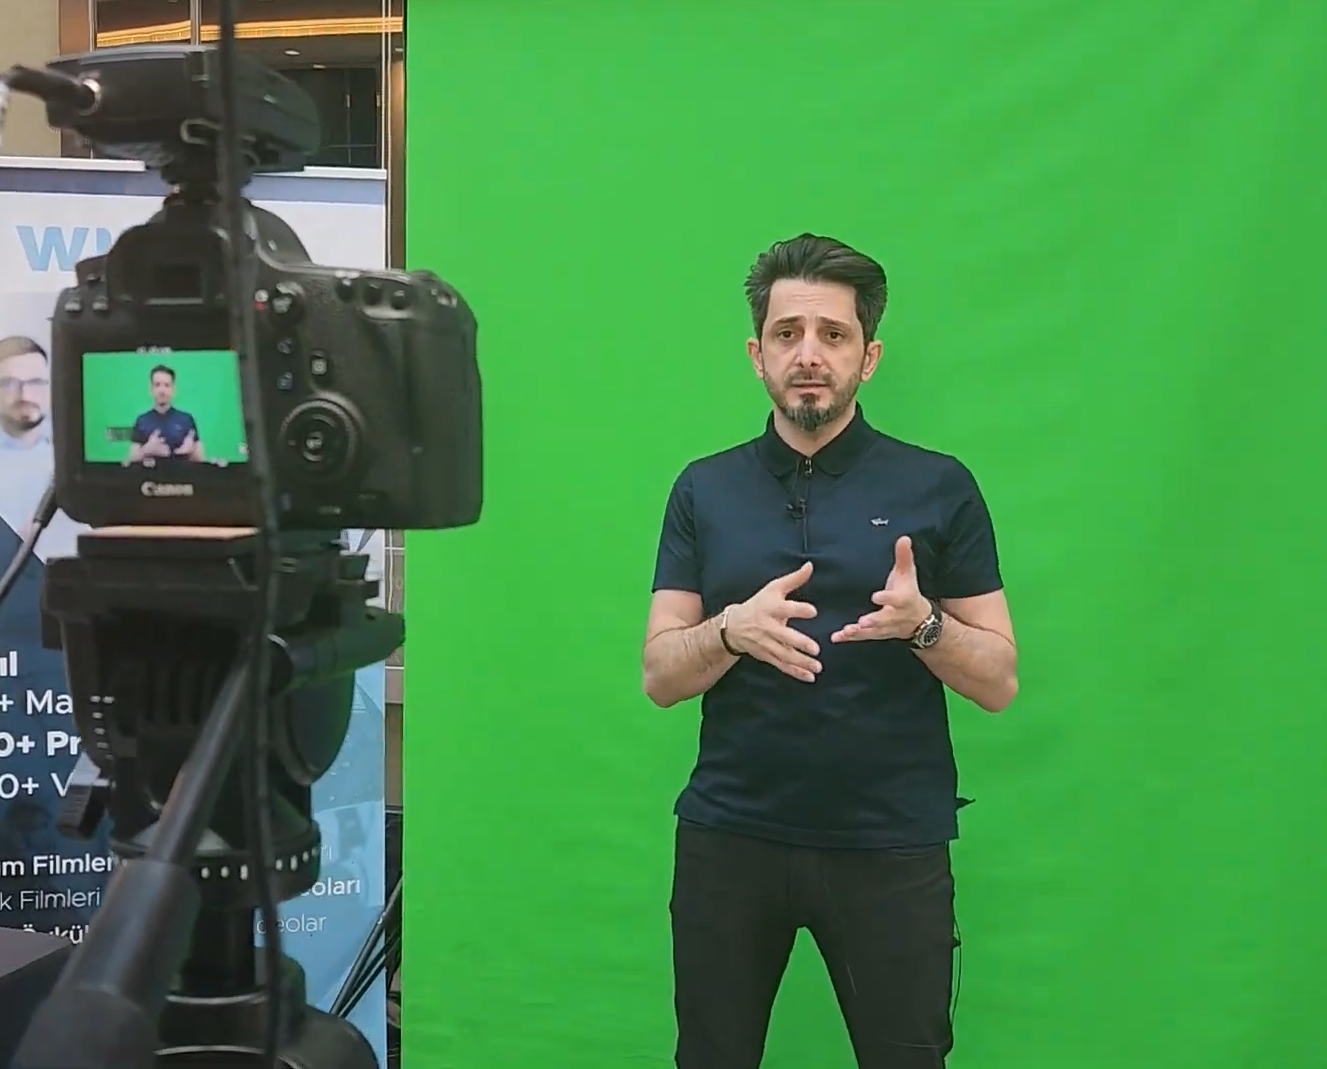
In an interview with Wise TV, Hayat Holding CISO Murathan Gemicioğlu discusses in detail the weak links at the endpoint, user behaviors, insider threats, and strategies regarding threat hunting.
Endpoint security is an area where we directly engage with the human element—often the weakest link in security and our primary point of contact. Consequently, when securing endpoints, we strive to protect users—who may have little technical expertise—against a portfolio of attackers employing a wide range of emerging techniques and tactics. There is no product, service, or device in the world where, upon setup, the user isn’t required to say, “Hello, here is my username and password.” No technology exists to eliminate this step entirely. Therefore, we must first educate people; only after educating them do we attempt to protect them using technology. We also need to guard against well-intentioned users who are simply trying to accomplish tasks quickly. Furthermore, insider threats have been on the rise in recent years. Thus, we must treat internal threats with the same level of scrutiny as external ones. Internally, we need to identify critical threats by leveraging artificial intelligence and behavioral analysis to monitor everything—from running services and drivers to user actions—and interpret these behaviors. In this context, it is crucial to recognize attack patterns and ensure they are regularly updated in the system. Conducting precise threat hunting—analyzing alarms generated by the services or internal resources interacting with the endpoint device—requires significant knowledge and experience. We need to establish robust frameworks and operations in these areas. We are discussing many concepts, such as Zero Trust and similar architectures. We strive to implement numerous measures to maintain the same level of security for people, whether they are at the office or at home. While awareness is paramount, we also need to support it with technology. We can achieve this by enhancing the knowledge of security teams and dedicating significant time to threat hunting.
The Importance of Endpoint Security
Endpoint security is one of the most critical components of cybersecurity in the modern business world. User devices are considered the weakest link in the network and are, therefore, attractive targets for attackers. Endpoint security refers to the measures taken to protect these devices, ensuring that both individuals and organizations are safeguarded against cyber threats.
The Role of the Human Factor
The human factor, often regarded as the weakest link in security, plays a critical role in endpoint security. Raising user security awareness establishes the first line of defense against cyberattacks. Training and awareness programs help users recognize security threats and take preventive measures against them.
Balancing Technology and Training
A balance between technology and training must be struck in endpoint security. While technology provides the necessary tools to protect users, training ensures that users employ these tools effectively. This balance is crucial for the success of cybersecurity strategies.
Internal and External Threats
Endpoint security must provide protection against both internal and external threats. Internal threats refer to security vulnerabilities caused—intentionally or unintentionally—by users within the organization. External threats encompass cyberattacks originating from outside sources. Effective strategies must be developed to address both types of threats.
Artificial Intelligence and Behavioral Analysis
Artificial intelligence and behavioral analysis play a significant role in endpoint security. By monitoring user behavior, these technologies detect anomalous activities and identify potential threats in advance. This establishes a proactive defense mechanism against cyberattacks.
Zero Trust Approach
Zero Trust is a novel approach to security architecture that operates on the principle of “never trust, always verify” for every user and device. This approach necessitates the continuous verification and monitoring of users and devices. Zero Trust is an effective strategy for enhancing endpoint security.
The Role of Security Teams
Security teams play a critical role in ensuring endpoint security. These teams develop security policies, monitor threats, and educate users. Enhancing the knowledge of security teams and allowing them to dedicate more time to threat hunting contributes to strengthening endpoint security.
Summary
Endpoint security is a cornerstone of cybersecurity and is of critical importance to both individuals and organizations. Key elements in ensuring endpoint security include the balance between the human factor, technology, and training; protection against internal and external threats; the use of artificial intelligence and behavioral analysis; the Zero Trust approach; and the role of security teams. Effectively integrating these elements creates a robust defense mechanism against cyber threats.
About the Wise
Similar Videos from this Wise
What roadmap should be followed for the security of critical infrastructure?
Why are IoT and OT security so critical? Murathan Gemicioğlu, CISO of Hayat Holding, discussed cybersecurity threats in [&hel...
To what extent is it possible to ensure endpoint security using a zero-trust approach?
Murathan Gemicioğlu, CISO of Hayat Holding, explained the Zero Trust philosophy—one of the most significant approaches in the...